AI is changing cybersecurity on both sides of the battlefield. The FBI has warned that threat actors are abusing an autonomous penetration-testing framework called ARTEX to automate several stages of cyber intrusions—from reconnaissance and vulnerability discovery to privilege escalation and data theft. The concern is not simply that hackers are using AI. It is that a coordinated set of software agents can move through attack steps quickly, repeatedly and at scale.
In an advisory dated 13 November 2026, the FBI said some intrusions using ARTEX progressed from initial targeting to privileged access in under three hours. The bureau also described campaigns affecting multiple industries and urged organizations to strengthen protections around internet-facing applications, cloud environments and third-party systems.
What is ARTEX AI?
ARTEX is an AI-driven, agentic penetration-testing framework. In simple terms, it is software designed to coordinate AI agents that can carry out tasks commonly found in security testing. It connects to external large language models (LLMs), rather than being a standalone AI model with its own built-in intelligence.
In an authorized security assessment, automation can help defenders identify weaknesses and validate their security controls. The same capabilities can be abused when an operator points the framework at systems without permission. The FBI says malicious actors have weaponized ARTEX to automate multiple phases of intrusions.
How can ARTEX be used in a cyberattack?
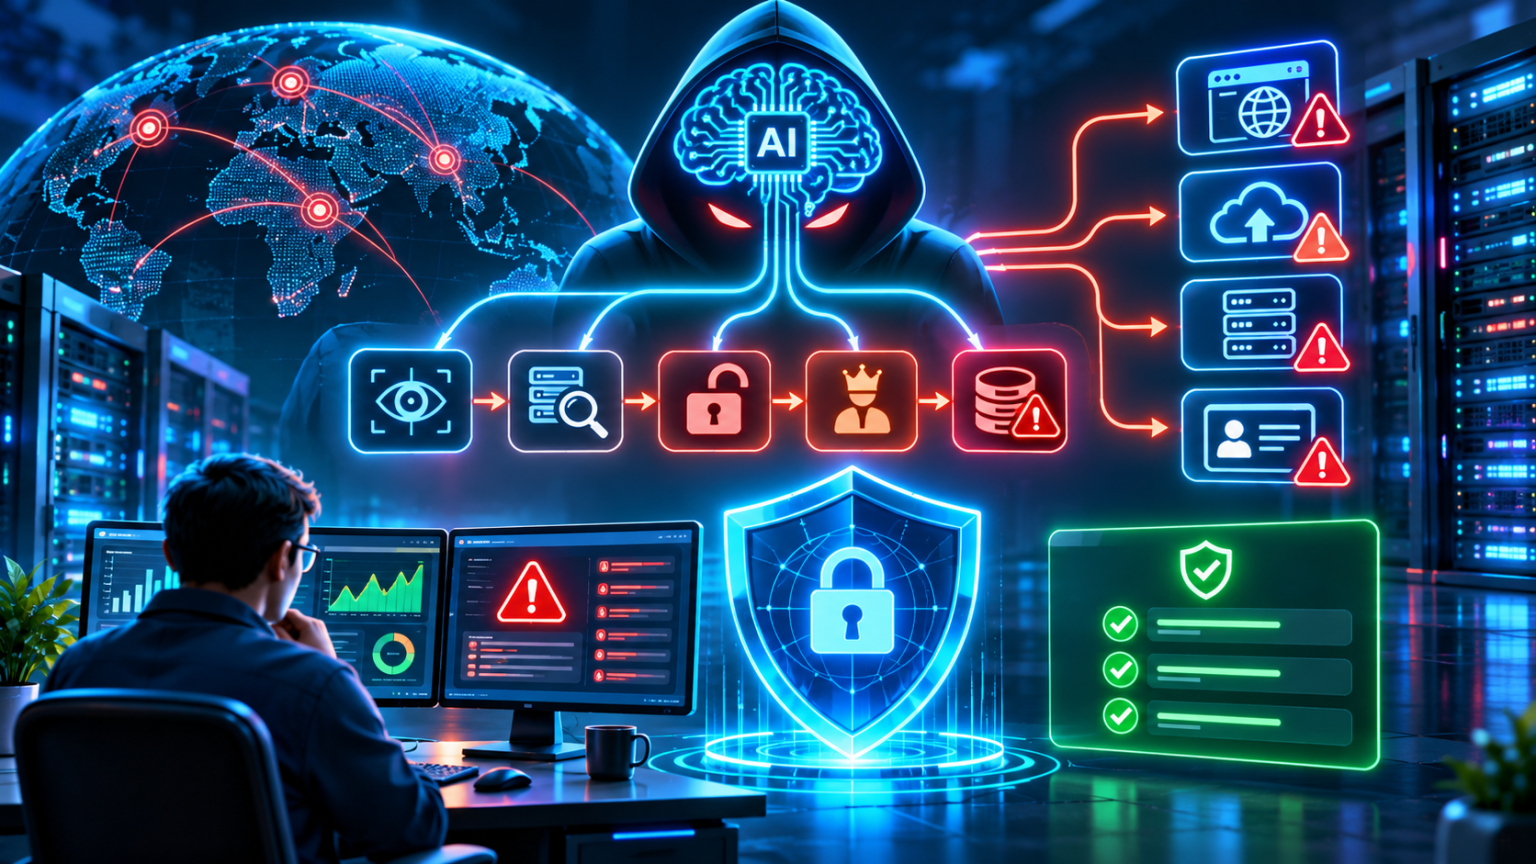
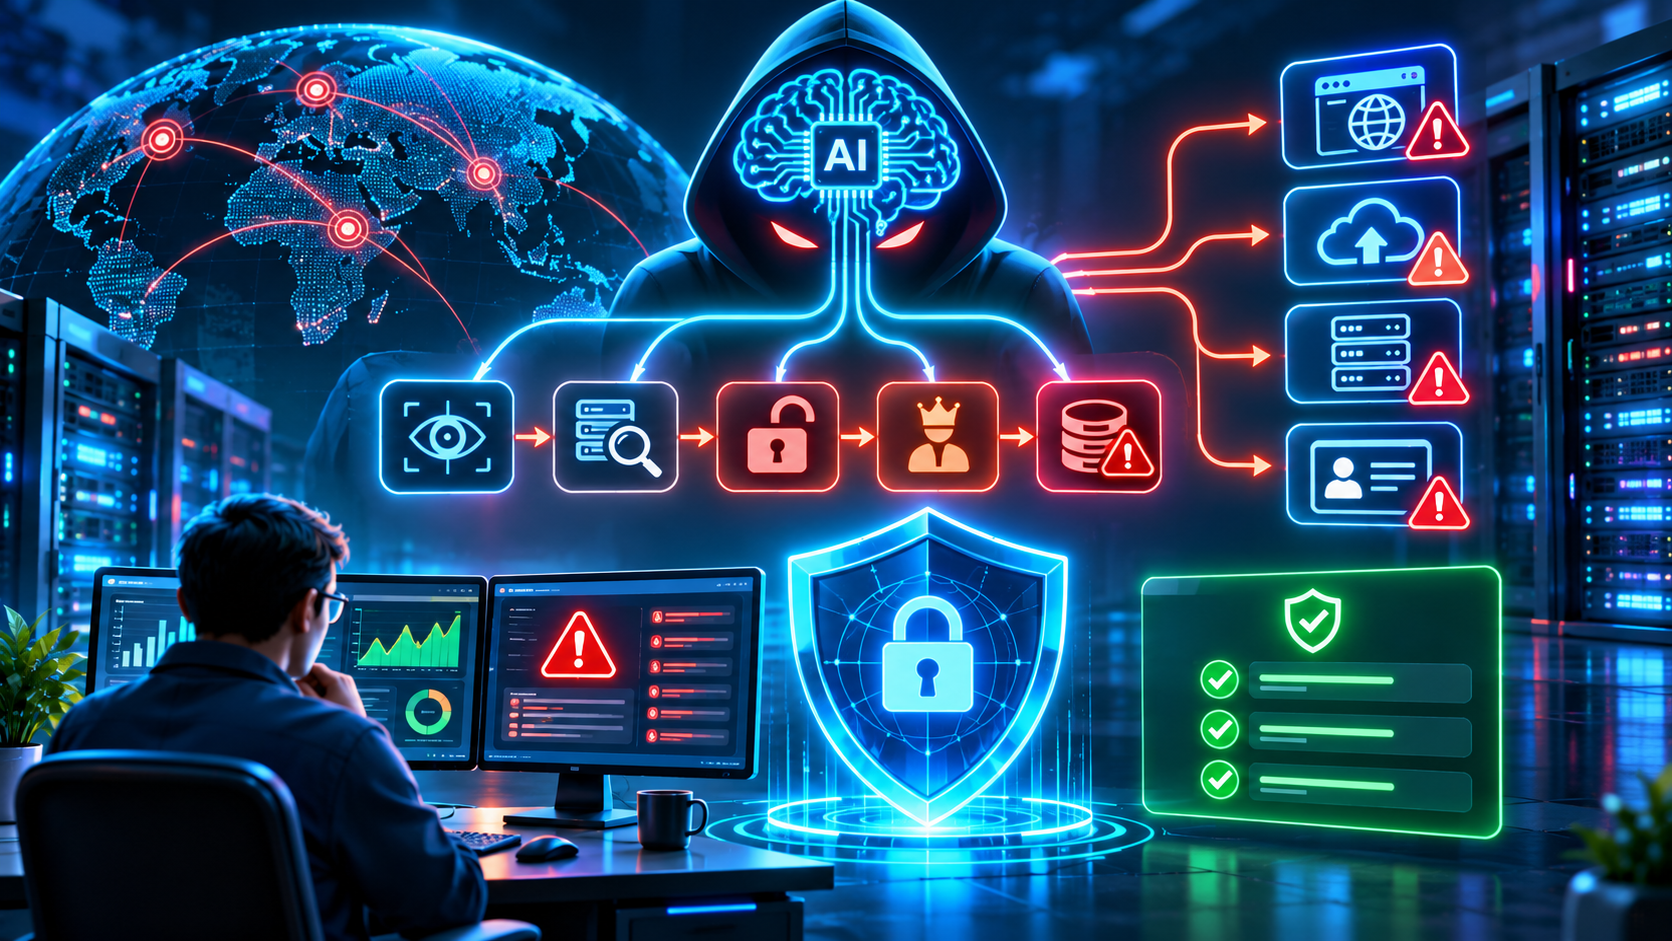
Rather than manually performing every step, an operator can give the framework a goal and let specialized agents coordinate tasks. Depending on the configuration and the target, an intrusion workflow may include:
- Reconnaissance: mapping exposed services, applications and potential entry points.
- Discovery: looking for misconfigurations, vulnerable software and weak access controls.
- Exploitation: attempting to take advantage of weaknesses that can be reached.
- Privilege escalation: seeking access with greater permissions after an initial foothold.
- Data access and exfiltration: attempting to collect and transfer information from compromised environments.
These are attack stages described in the context of the FBI advisory—not a guarantee that ARTEX can successfully complete every stage against every target. Outcomes depend on the environment, available vulnerabilities, credentials, security controls and the operator’s actions.
Why has the FBI issued a warning?
The FBI’s 13 November FLASH advisory says malicious cyber actors have used ARTEX since at least August 2026 against organizations in sectors including financial services, government, technology, defense, semiconductors, energy, healthcare, manufacturing, telecommunications and legal services.
Three points make the warning especially important:
- Speed: the FBI says some intrusions reached privileged access in under three hours. This is a reported finding from certain incidents, not a universal attack timeline.
- Scale: automation can allow operators to run activity against multiple organizations at once, potentially increasing the number of targets and the pace of activity.
- Less obvious entry points: partner portals, supplier systems, employee applications, mobile backends, legacy services and third-party integrations can be overlooked compared with an organization’s main website.
What incidents did the FBI highlight?
The advisory describes financially motivated attacks against South Korean financial institutions in which personal information relating to approximately 67,000 individuals was reportedly exfiltrated. It also discusses a supply-chain compromise involving ConnectWise Cloud Backup customers. In that campaign, attackers used compromised application identities and attempted authentication against more than 2,250 downstream Microsoft 365 tenants.
These figures describe incidents and attempted downstream access cited in the advisory. They should not be read as proof that every tenant was successfully compromised.
Is ARTEX still available?
The FBI says the original developer removed the public GitHub repository in October 2026 after malicious use came to light. That did not make the framework disappear. The advisory says it continued to circulate through community forks, archived copies, localized variants and a commercial version known as ARTEX PRO. Researchers had identified more than 1,600 publicly exposed ARTEX console instances by early November, according to the FBI advisory.
Removing one repository therefore does not remove copies already downloaded, modified or redistributed. Organizations should focus on defending their systems rather than assuming the threat has ended because the original repository is no longer public.
What should businesses and hosting providers do?
The FBI’s recommendations point to a practical security programme. Website owners, hosting providers, IT teams and cloud administrators should prioritize the following actions:
- Inventory every internet-facing service. Include websites, APIs, control panels, partner portals, employee apps, staging systems, legacy services and third-party integrations. Unknown assets are difficult to protect.
- Restrict administrative access. Put hosting control panels, SSH, RDP, backup consoles and cloud administration interfaces behind trusted networks, VPNs or zero-trust access controls. Do not expose management interfaces unnecessarily.
- Strengthen identity security. Enforce multifactor authentication, remove unused accounts, rotate exposed credentials and review service-principal or application permissions. Apply least privilege to every account and integration.
- Patch and harden exposed applications. Keep operating systems, CMS platforms, plugins, themes, frameworks and server software updated. Remove abandoned components and fix insecure configurations.
- Monitor for unusual automation. Investigate sudden bursts of requests, repeated authentication failures, unusual API usage, unexpected outbound connections to AI model providers, new administrator accounts and unexplained privilege changes.
- Protect backups and recovery systems. Use isolated or immutable backups where possible, restrict backup administration and regularly test restoration procedures.
- Watch third-party access. Review supplier connections, OAuth grants, application identities, API keys and integrations. A trusted vendor account can become a route into customer environments.
- Prepare an incident-response plan. Know how to isolate affected systems, preserve logs, revoke credentials and tokens, notify customers where required, and report suspected cybercrime to the appropriate authorities.
For hosting businesses in particular, a useful starting point is to review exposed control panels and management ports, enforce MFA for customer and administrator accounts, monitor login and API activity, separate customer environments, and verify that backups cannot be altered using the same credentials as production systems.
Does this mean AI models such as ChatGPT are hacking websites?
No. The FBI advisory describes a framework that can connect to external AI models and be directed by threat actors. It does not say that a general-purpose AI service independently selected victims or launched these campaigns. The important distinction is between an AI model and the software, tools, permissions and human operator that assemble it into an automated workflow.
AI can also help defenders: security teams can use automation to triage alerts, analyze logs and identify weaknesses in authorized environments. The same technology can create risk when it is connected to offensive tools and used without authorization.
What should website owners do right now?
Start with the basics: check for outdated software, remove unused plugins and accounts, enable MFA, restrict administrative access, review recent login and API logs, and confirm that backups are recoverable. If you operate a business website or hosting environment, include supplier portals and cloud integrations in the review—not just the public-facing homepage.
Do not rely on a single IP blocklist as your main defence. Indicators of compromise can change, and the FBI cautions that indicators need to be assessed in context. Layered controls, good logging and a tested response plan are more durable protections.
Final thoughts
The ARTEX warning is a reminder that cyber risk is evolving from isolated tools toward coordinated, AI-assisted workflows. The key issue is not that AI makes every attack unstoppable; it is that automation can compress the time defenders have to detect and contain an intrusion. Organizations that know what they expose, control who can access it, monitor identities and applications, and practise incident response will be in a stronger position.
Sources and further reading
- FBI IC3: Threat Overview of ARTEX Autonomous Penetration Testing Framework (13 November 2026)
- BleepingComputer: FBI warns ARTEX AI hacking tool is powering global cyberattacks
- TechCrunch: FBI says ARTEX AI tool used to breach networks in under three hours
- Reuters: ARTEX developer changes project availability after Korean bank hack reports
Editorial note: This article summarizes the FBI advisory and reporting available as of 18 November 2026. ARTEX is discussed for awareness and defence; this article does not provide instructions for unauthorized access.