ARTEX was not originally presented as a cybercrime product. It was built as an AI-powered penetration-testing framework: a way for security professionals to automate parts of authorized security assessments. But tools designed to test systems can become dangerous when they are placed in the hands of criminals or state-aligned operators.
That is exactly the concern now surrounding ARTEX. The FBI says malicious actors have weaponized the framework to automate multiple stages of cyber intrusions, from reconnaissance to data theft. Security researchers have also linked ARTEX to financially motivated attacks and espionage campaigns, showing how quickly an AI-assisted security tool can become part of a much wider threat landscape.
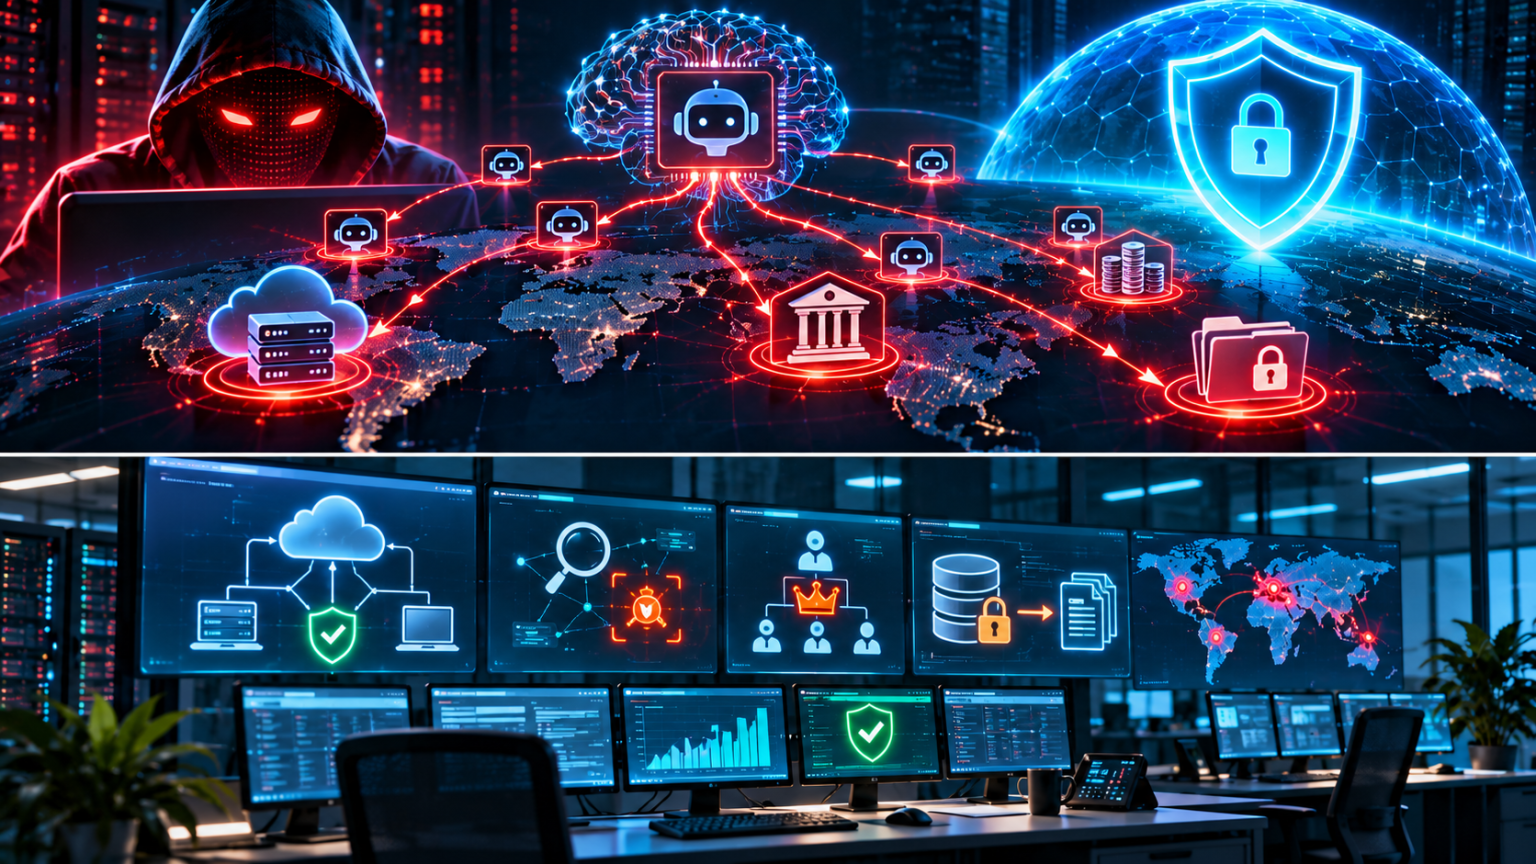
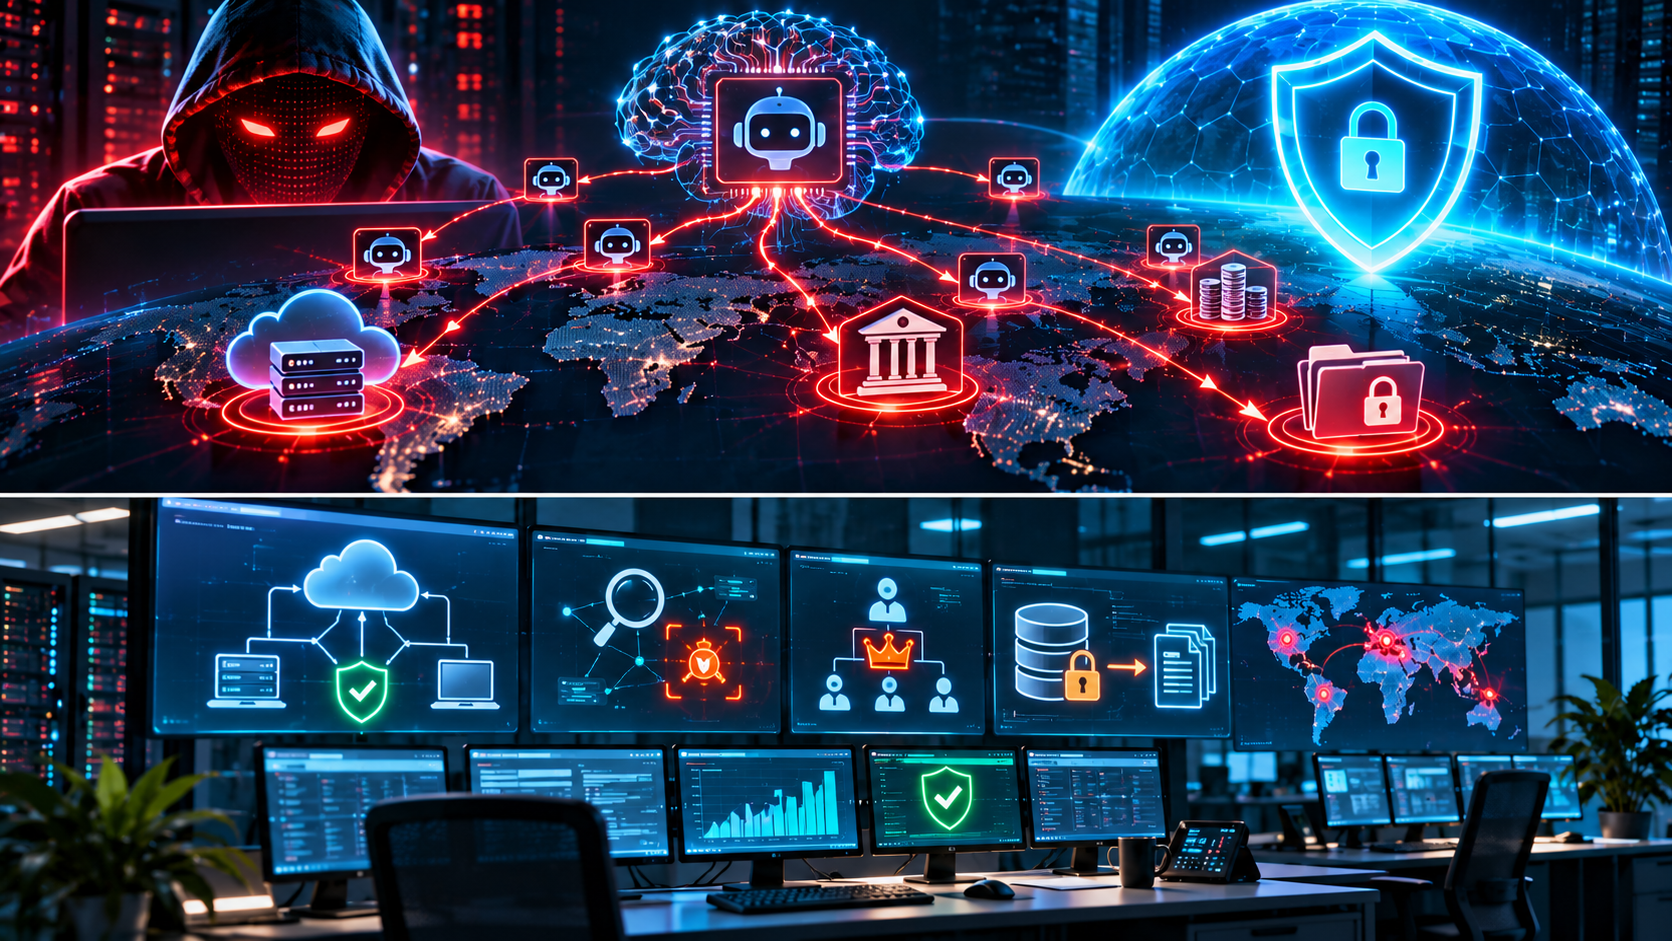
The important story is not simply that hackers are using AI. It is that ARTEX can coordinate multiple agents, connect to external language models and work through a sequence of technical tasks at a pace that gives defenders less time to react.
What is ARTEX?
ARTEX is an agentic, large-language-model-driven penetration-testing framework. Rather than being an AI model itself, it acts as an orchestration platform: it connects to external models and gives AI agents access to tools that can be used during security testing.
In legitimate hands, penetration-testing platforms help organizations discover weaknesses in systems they own or are authorized to assess. ARTEX was designed to automate parts of that work. Its agent-based architecture can coordinate activities such as reconnaissance, vulnerability discovery and validation, and other stages of a security assessment.
The risk appears when operators direct those capabilities at systems without permission. According to the FBI’s 13 November 2026 FLASH advisory, threat actors have used ARTEX to automate several phases of real intrusions, including activity that can lead to privilege escalation and data exfiltration.
Why is ARTEX different from a traditional hacking tool?
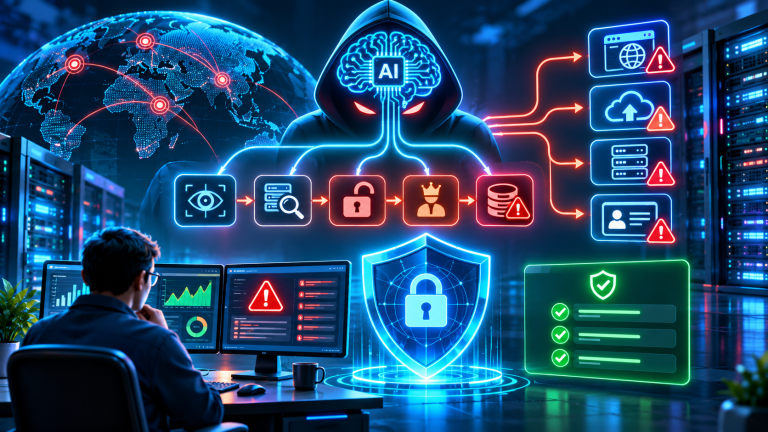
Traditional automation often follows a fixed script. It performs a defined sequence of actions, and a human operator decides what to do when the environment changes. An agentic framework can interpret results, choose another task, call tools and continue towards a broader objective.
ARTEX can coordinate multiple agents and connect them to external AI models. This does not make every operation fully independent: people still select targets, configure environments and set goals. But once a workflow is running, agents can carry out parts of the operation with less step-by-step human input.
The FBI says some intrusions progressed from initial targeting to privileged access in under three hours. That figure relates to cases described in the advisory; it is not a promise that every ARTEX operation succeeds or takes the same amount of time.
From security testing to cybercrime
The framework’s dual-use nature is central to the story. The same broad capabilities that can help a security team map its own attack surface can be abused to identify exposed systems, search for weak access controls and automate attempts to move deeper into a network.
The FBI says malicious use has been observed since at least August 2026 across sectors including financial services, government, technology, defence, semiconductors, energy, healthcare, manufacturing, telecommunications and legal services.
That range matters. The threat is not limited to one industry or one type of organization. Any business with exposed applications, cloud services, employee portals, supplier connections or poorly protected identities may have an attack surface worth examining.
ARTEX and espionage: what researchers have observed
ARTEX has drawn particular attention because security researchers have reported its use by both financially motivated groups and actors linked to state-aligned espionage activity.
In its 13 November report, SentinelOne described a China-nexus espionage actor using ARTEX against more than 200 organizations across at least 14 countries. The researchers said the operator directed agents to identify Windows hosts that lacked endpoint detection and response (EDR) coverage. SentinelOne also assessed that at least five threat actors or clusters had used ARTEX since late August, spanning espionage and financially motivated activity.
These are findings and assessments attributed to SentinelOne’s research, not a blanket conclusion that every ARTEX deployment is connected to a government. Attribution in cyber investigations is complex, and claims about state links should be read in the context of the evidence and confidence level stated by the researchers.
The South Korean financial-sector attacks
The FBI advisory describes financially motivated attacks against South Korean financial institutions in which personal information relating to approximately 67,000 individuals was reportedly exfiltrated.
The incidents demonstrate how automated reconnaissance and exploitation can put pressure on organizations that rely on weak authentication, exposed services or incomplete monitoring. They also show why financial institutions need to look beyond perimeter security and pay close attention to identity protection, application permissions and unusual access patterns.
The ConnectWise supply-chain compromise
One of the most consequential cases discussed by the FBI involved ConnectWise Cloud Backup and downstream Microsoft 365 environments. The advisory says the compromise enabled access attempts against more than 2,250 downstream tenants.
This is a supply-chain problem: customers may depend on a trusted service provider or application identity, and that relationship can become a route into their own environment if the provider’s credentials or permissions are compromised. The figure of more than 2,250 refers to downstream tenants involved in attempted authentication, not proof that every one of those tenants was successfully breached.
For businesses, the lesson is straightforward. Third-party access, OAuth grants, application identities, backup integrations and service accounts deserve the same scrutiny as employee administrator accounts.
How ARTEX became widely available
The original ARTEX project was made publicly available in 2026. After reports of malicious use, its developer removed the original GitHub repository in October and ended public development of the open-source release.
That did not make the framework disappear. The FBI says copies continued to circulate through community forks, archived repositories, localized variants and a commercial version known as ARTEX PRO. SentinelOne’s research also describes maintained forks and alternative projects in the wider ecosystem.
Researchers identified more than 1,600 publicly exposed ARTEX console instances by early November, according to the FBI advisory. Exposed consoles are a security concern in their own right: management interfaces should never be left publicly accessible without strong authentication and appropriate network restrictions.
Why the use of external AI models matters
ARTEX does not contain one proprietary AI brain that independently performs every task. It can connect to external large language models, including commercial and open-weight models. The selected model provides reasoning and language capabilities, while the framework supplies the workflow and access to tools.
This distinction is important. A model provider is not automatically responsible for an attack simply because an attacker connected its model to an offensive framework. The operator’s intent, the framework’s configuration, the tools made available and the target’s security controls all matter.
It also creates a cost and access issue. Researchers have reported that some operators used relatively inexpensive model configurations and default settings. That can lower the financial and technical barriers for groups that want to run multiple operations at once.
What should organizations look for?
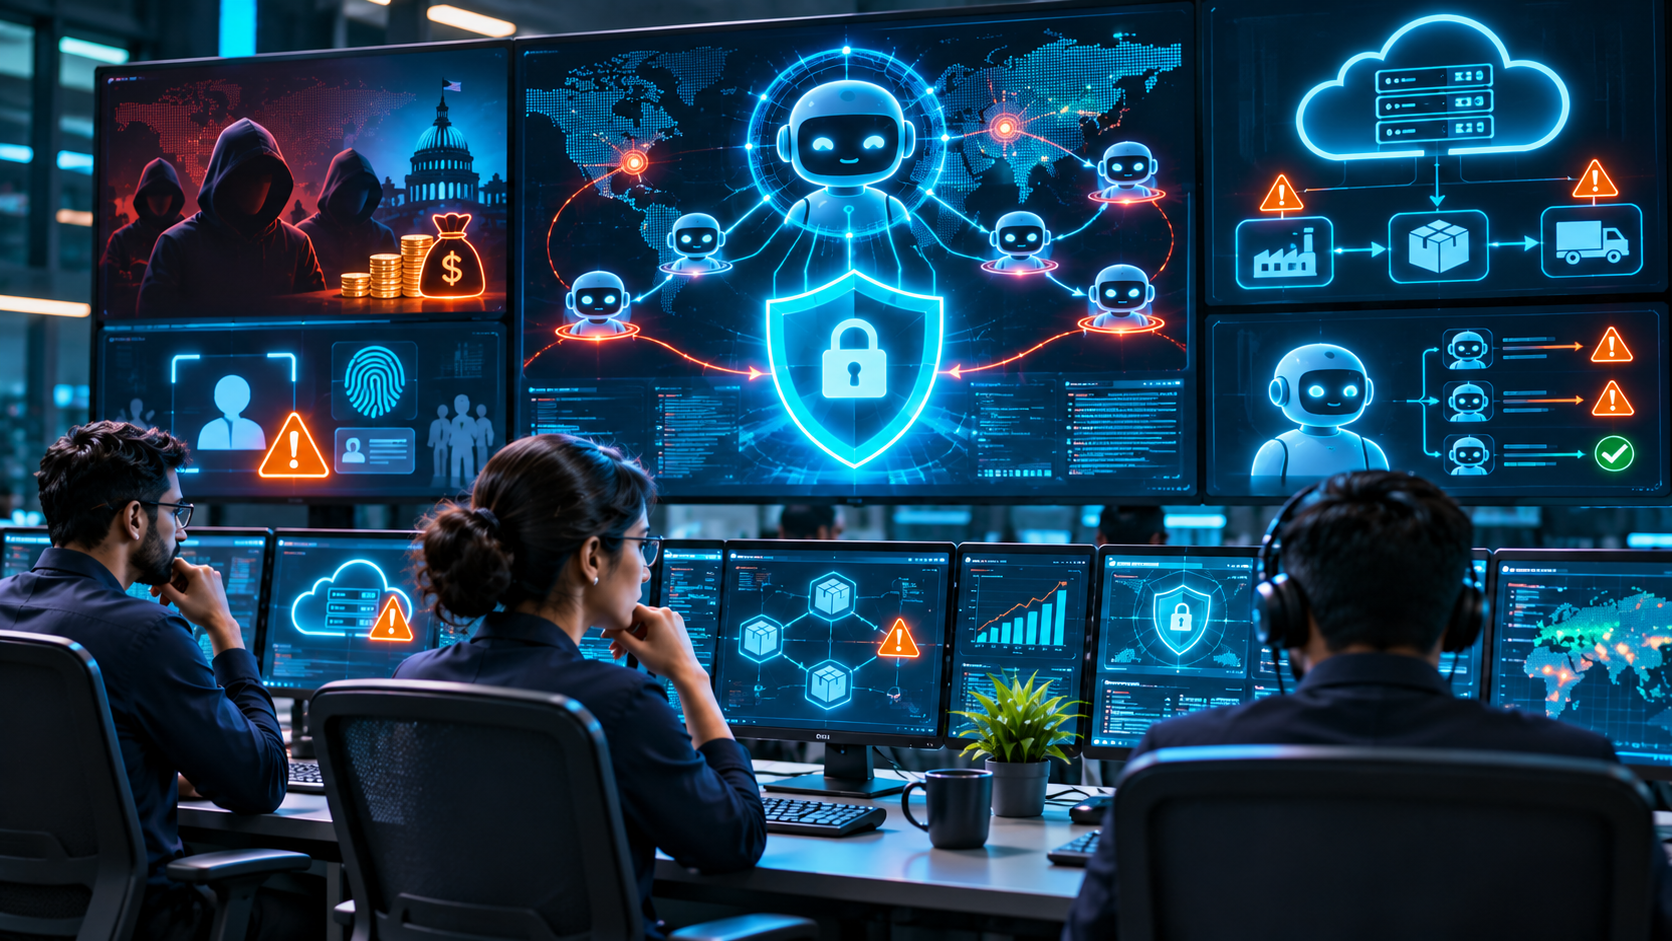
The FBI advisory includes technical indicators and mitigation guidance. Organizations should consult the original advisory and work with their security teams before treating any single indicator as proof of compromise. IP addresses and other infrastructure details can change, and isolated alerts can have legitimate explanations.
At a practical level, defenders should investigate patterns such as:
- Unexpected bursts of automated requests against public websites, APIs or self-service portals.
- Unusual authentication attempts across multiple accounts, tenants or cloud applications.
- Unexpected changes to application permissions, service principals, OAuth grants or privileged roles.
- New or unexplained access to cloud secrets, key vaults, backup systems or sensitive data stores.
- Unusual outbound transfers, especially after suspicious identity or privilege events.
- Management consoles, staging systems or administrative interfaces exposed directly to the internet.
- Missing endpoint protection on servers or workstations that should be monitored.
How to defend against ARTEX-enabled attacks
There is no single product or blocklist that can stop every agentic attack. The strongest response is a combination of good security hygiene, continuous monitoring and a plan that allows teams to act quickly.
- Secure internet-facing applications. Review public websites, APIs, mobile backends, partner portals, employee tools and legacy services. Remove systems that are no longer needed and fix exposed vulnerabilities.
- Enforce multifactor authentication. Protect administrator accounts, cloud consoles, remote access and third-party integrations. Use phishing-resistant MFA where practical.
- Review application identities. Audit service principals, OAuth grants, API keys and automation accounts. Remove excessive permissions and rotate credentials that may have been exposed.
- Apply least privilege. Give each user, service and automation process only the access it needs. Separate backup administration from production administration.
- Keep EDR coverage complete. Ensure endpoints and servers are monitored. Investigate devices where security agents are missing, disabled or not reporting.
- Monitor cloud and identity activity. Collect authentication, application, API, key-vault and administrative logs centrally. Alert on unusual privilege changes and access patterns.
- Protect supplier relationships. Review vendor access, backup integrations, remote support tools and multi-tenant applications. Know how to revoke a third-party connection quickly.
- Rate-limit sensitive interfaces. Apply sensible limits and anomaly detection to login pages, APIs and account-recovery flows without relying on rate limiting as the only control.
- Prepare for rapid containment. Have tested procedures to revoke tokens, disable compromised identities, isolate affected systems and preserve evidence.
- Maintain recoverable backups. Keep isolated or immutable copies where possible, protect backup credentials and regularly test restoration.
What hosting providers and WordPress site owners should do
Hosting providers manage infrastructure and access paths used by many customers. A compromised management account or shared service identity can create consequences beyond a single website.
Hosting teams should restrict WHM, control panels, SSH and other management interfaces to trusted networks where possible; enforce MFA for administrators and resellers; separate customer environments; monitor unusual logins and API activity; and protect backup systems with independent credentials.
WordPress site owners should keep WordPress core, themes and plugins updated, remove unused administrator accounts, enable MFA, use unique credentials and maintain independent backups. Review application passwords, API integrations and any plugin that has access to sensitive site data. A small business website can still be an entry point into a wider hosting or supplier environment.
Does ARTEX mean AI can hack any organization?
No. AI does not remove the need for an exploitable weakness, valid credentials, misconfiguration or a path into the target environment. Agents can fail, make incorrect decisions, trigger alarms or be blocked by well-designed controls.
But ARTEX shows why organizations should not rely on attackers being slow, highly skilled or limited to one target at a time. Automation can make familiar techniques faster and more repeatable. The right response is to reduce the opportunities available to an attacker and make suspicious activity easier to detect.
Final thoughts: ARTEX is a warning about the next phase of cybercrime
ARTEX began as a framework associated with automated security testing. Its adoption by malicious actors has turned it into a case study in the risks of agentic AI. The FBI’s warning, together with research from SentinelOne and other security firms, shows that these capabilities are already being tested and used in real-world campaigns.
The bigger lesson extends beyond ARTEX. Similar agentic frameworks will continue to appear, and removing one repository will not remove the underlying capabilities. Businesses need to protect identities, reduce exposed services, monitor cloud and supplier access, and rehearse incident response before an intrusion happens.
In this new environment, strong security is not about guessing which AI tool an attacker will use next. It is about making sure that when automated tools arrive, they cannot move freely through your systems.
Sources and further reading
- FBI IC3: Threat Overview of ARTEX Autonomous Penetration Testing Framework (13 November 2026)
- SentinelOne: ARTEX Unmasked – The Rise of AI-Powered ARTEX in Cybercrime & Espionage (13 November 2026)
- TechCrunch: FBI says ARTEX AI tool used to breach networks in under three hours (16 November 2026)
- Palo Alto Networks Unit 42: ARTEX and AI-Powered Red Teaming Tools – What Defenders Need to Know
- BleepingComputer: FBI warns ARTEX AI hacking tool is powering global cyberattacks
Editorial note: This article is an original, reader-friendly overview based on the FBI advisory and public security research available as of 18 November 2026. Findings about espionage attribution and individual campaigns are attributed to the researchers who reported them. It is intended for cybersecurity awareness and defence.