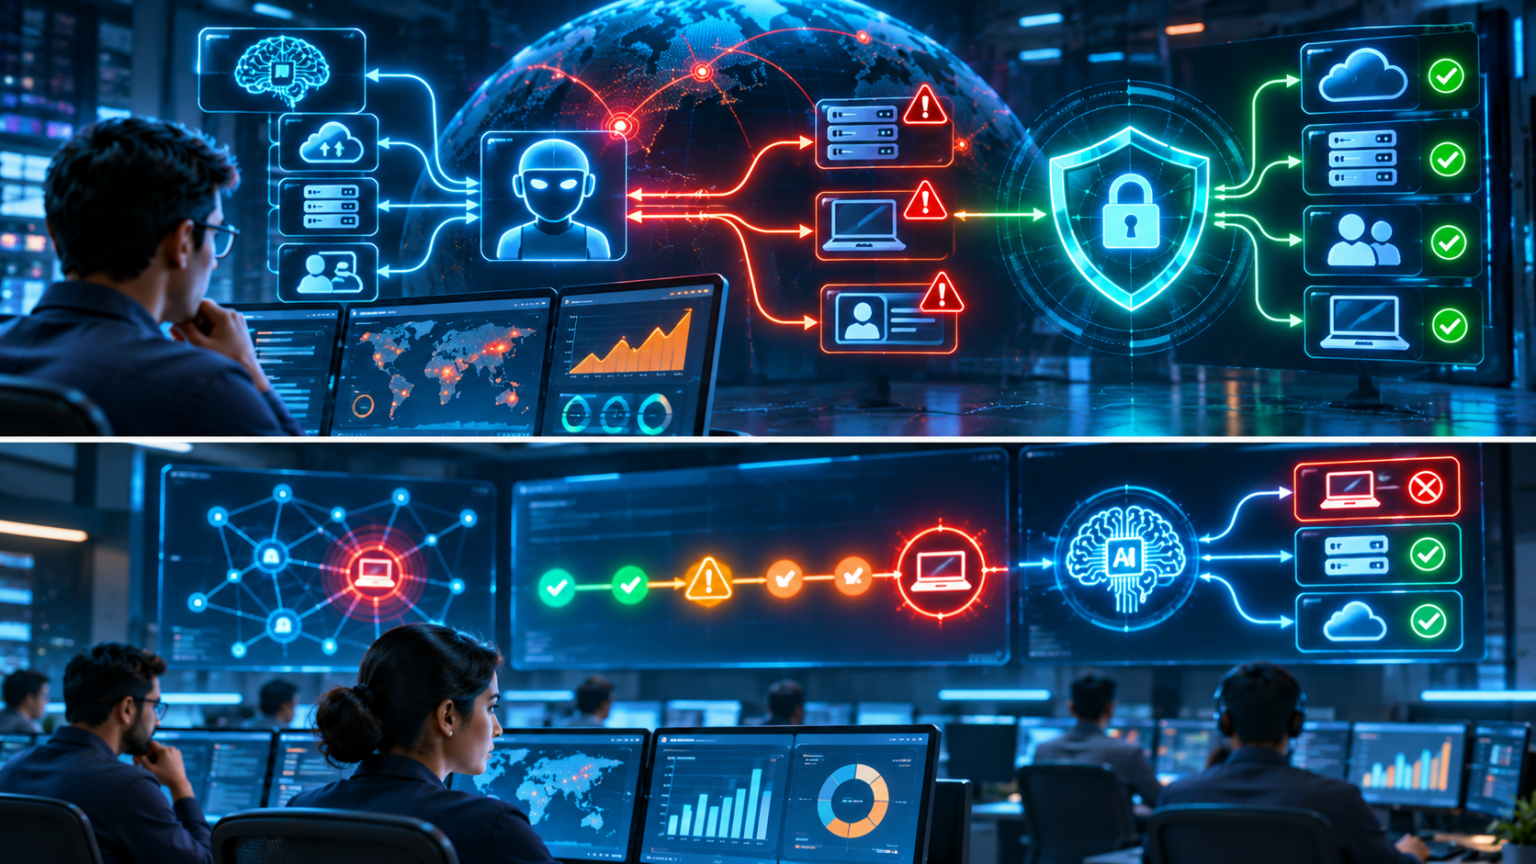
Cybersecurity has always been a race against time. An attacker finds a weakness, tries to get inside, and looks for a way to move deeper into a network. Defenders must spot the activity, understand what is happening and stop it before damage is done.
Artificial intelligence is changing the pace of that race. Criminal groups are using AI to research targets, write and adapt code, process stolen information and coordinate multiple tasks. Security teams are using AI too, but they still have to make sure the technology is accurate, properly controlled and connected to the systems that need protecting.
So the question is no longer simply whether AI will be used in cyberattacks. It already is. The bigger question is whether defenders can reduce the time between detecting a threat and taking effective action.
AI is changing the speed of cyberattacks
Attackers do not necessarily need a completely new type of malware to become more dangerous. AI can make familiar techniques faster, easier to adapt and cheaper to repeat.
For example, a criminal can use AI to draft convincing phishing messages, summarize information gathered about a target, help write scripts, examine exposed services or organize stolen credentials. More advanced agent-based workflows can split a job into smaller tasks and let several automated agents work on them at the same time.
That does not mean every attack is fully autonomous. Human operators still choose targets, set objectives and make decisions in many real-world intrusions. The important change is that AI can reduce the amount of manual work required between those decisions.
What the latest cybersecurity reports are telling us
Several 2026 threat reports point to the same trend: automation is reducing the time attackers need to prepare and execute parts of an operation.
- CrowdStrike: its 2026 Global Threat Report said AI-enabled adversary operations increased 89% year over year. It also reported an average eCrime breakout time of 29 minutes in 2025, with the fastest observed breakout taking 27 seconds. Breakout time measures movement after initial access; it is not a measure of how long every AI attack takes.
- Google Threat Intelligence Group: in a September 2026 update, Google described a case in which a threat actor compromised cloud resources and then used an agent-enabled workflow to plan, build and execute a mass credential-harvesting campaign in under six hours.
- Microsoft: its 2026 Digital Defense Report said the median time from vulnerability discovery in the wild to weaponization had fallen to well below 24 hours. Microsoft also emphasized that AI-assisted attacks are not all fully autonomous and that many complex intrusions still involve human direction.
- SANS: its 2026 AI in Cybersecurity research reported that 78% of surveyed organizations had confirmed or suspected AI-enabled attacks. The survey also found that 63% of practitioners reported significant shortcomings in AI threat detection.
These findings come from different research methods and measure different things. They should not be combined into one universal attack-speed statistic. Taken together, however, they show why security teams are reassessing how quickly they can detect, investigate and contain suspicious activity.
How attackers are using AI
1. More convincing social engineering
AI can help criminals write messages that sound natural, adapt them to a person’s role or organization, and produce content in different languages. Voice cloning and synthetic media can also make impersonation attempts more believable. The technology does not make every message convincing, but it can make large-scale personalization easier.
2. Faster reconnaissance and research
Before attempting an intrusion, attackers often collect information about an organization, its technology and its people. AI can help sort public information, summarize technical documentation and organize potential targets. That can shorten preparation time, especially when combined with existing scanning and automation tools.
3. Quicker development and adaptation
AI coding assistants can help generate or modify scripts and analyze errors. In malicious hands, that capability can support the development and adjustment of tools used in an attack. It can also help operators understand unfamiliar environments faster.
4. Coordinated agent workflows
Agentic systems can divide a broader objective into smaller tasks, pass information between agents and retry when a step fails. Google reported observing this kind of multi-agent activity in a credential-harvesting campaign. It is a significant development, but it should not be confused with a claim that all cyberattacks now run independently from start to finish.
5. Attacks on AI systems themselves
AI applications create new assets that need protection: model endpoints, API keys, service identities, retrieval databases, plugins, connectors and agent permissions. Attackers may target these components to access sensitive information or use an AI system as a stepping stone into other services.
Why defenders can struggle to keep up
Security teams already deal with huge volumes of alerts, logs and vulnerability reports. Faster attacks make the workload harder, but speed is only part of the problem.
- Too many alerts: analysts can lose time investigating false positives while genuine incidents continue.
- Fragmented tools: endpoint, identity, email, cloud and network systems may each hold only part of the evidence.
- Slow remediation: a vulnerability may be weaponized quickly, while testing and deploying a fix across a large organization can take much longer.
- Overprivileged identities: stolen credentials, API keys and service accounts can provide access that looks legitimate to monitoring systems.
- Third-party exposure: suppliers, SaaS platforms and software dependencies can create routes into an organization that its security team does not fully control.
- Unmanaged AI tools: employees may connect unapproved assistants, agents or plugins to company data and systems.
Adding an AI security product does not automatically solve these problems. If alerts are disconnected, permissions are excessive or response procedures are unclear, automation can simply make a confusing process run faster.
Can AI help defenders respond at machine speed?
Yes—when it is used with clear limits and good security foundations. Defensive AI can summarize alerts, connect related events, identify unusual patterns, help prioritize vulnerabilities and recommend response steps. In some carefully controlled environments, automated systems can isolate an endpoint, disable a compromised token or block a suspicious connection.
The goal is not to remove human analysts. It is to let them spend less time collecting and formatting evidence and more time making important decisions. High-impact actions should have appropriate approval, safeguards and audit trails.
What businesses should do now
Organizations do not need to wait for a fully autonomous attack to improve their security. The following steps address the weaknesses that attackers commonly exploit, whether AI is involved or not.
- Know what is exposed. Maintain an up-to-date inventory of websites, servers, APIs, cloud resources, remote-access services, development systems and third-party connections.
- Secure identities first. Require multifactor authentication, remove dormant accounts, use phishing-resistant authentication where practical, rotate exposed secrets and apply least privilege to users and service accounts.
- Patch internet-facing systems quickly. Prioritize actively exploited and critical vulnerabilities. Use a risk-based process that includes emergency patching, compensating controls and verification.
- Improve visibility across environments. Centralize useful logs from endpoints, identity providers, email, firewalls, cloud platforms and applications. Ensure logs are retained long enough to investigate incidents.
- Protect AI tools and agents. Inventory approved AI services, restrict what agents can access, protect API keys, review connectors and prevent untrusted input from triggering sensitive actions.
- Automate safe first responses. Prepare tested playbooks for actions such as disabling a compromised account, revoking a token or isolating a device. Set approval requirements for actions that could disrupt critical operations.
- Segment important systems. Limit the ability of an intruder to move from a user device into backups, production databases, management networks or cloud control planes.
- Test recovery, not just prevention. Keep isolated or immutable backups where possible, practise restoration and make sure incident responders know who can authorize emergency decisions.
- Train employees for AI-enabled scams. Teach staff to verify unusual payment requests, unexpected password resets, voice instructions and requests to share credentials or sensitive files.
What this means for web hosting providers
Hosting companies manage infrastructure that customers depend on, which makes account security and isolation especially important. A compromised hosting administrator account can have consequences far beyond one website.
Hosting providers should protect control panels and SSH access with MFA and network restrictions, monitor unusual login patterns, separate customer environments, restrict reseller and support privileges, secure backup systems and review API tokens used by automation. They should also keep operating systems, control panels, billing platforms and customer-facing applications patched.
Customers can help by using unique passwords, enabling MFA, keeping CMS software and plugins updated, removing unused administrator accounts and maintaining independent backups. Security is strongest when providers and customers both take responsibility.
Will AI replace cybersecurity professionals?
Not in the foreseeable future. AI can process information and carry out bounded tasks at a speed that is difficult for people to match. But security work also involves understanding business impact, judging incomplete evidence, coordinating teams and deciding when an action is too risky.
As AI takes over more repetitive work, the role of security professionals is likely to shift toward oversight, investigation, architecture, threat hunting and governance. Teams will need people who understand both security fundamentals and the behaviour and limitations of AI systems.
So, can defenders keep up?
They can—but not by relying on manual processes alone, and not by buying AI tools without changing how security operations work. Defenders need continuous visibility, strong identity controls, rapid vulnerability management and rehearsed incident response. AI can help connect the signals and accelerate safe actions, while people remain accountable for critical decisions.
The most important lesson is that attackers do not need a futuristic, fully autonomous system to cause serious damage. Even modest automation can make phishing, reconnaissance and credential abuse faster and easier to repeat. Businesses that strengthen their foundations now will be better prepared for whatever comes next.
Sources and further reading
- CrowdStrike 2026 Global Threat Report
- Google Threat Intelligence Group: AI Threat Tracker – From Prompting to Autonomy (8 September 2026)
- Microsoft 2026 Digital Defense Report
- SANS 2026 AI in Cybersecurity Research
- Sophos AI Security 2026 Report
Editorial note: This article reflects the cited research available as of 18 November 2026. Reported statistics refer to the specific datasets and definitions used by each organization; they are not universal measures of every cyberattack.